Application Integrity Verification In Multi-Tier Architectures
(57) Abstract
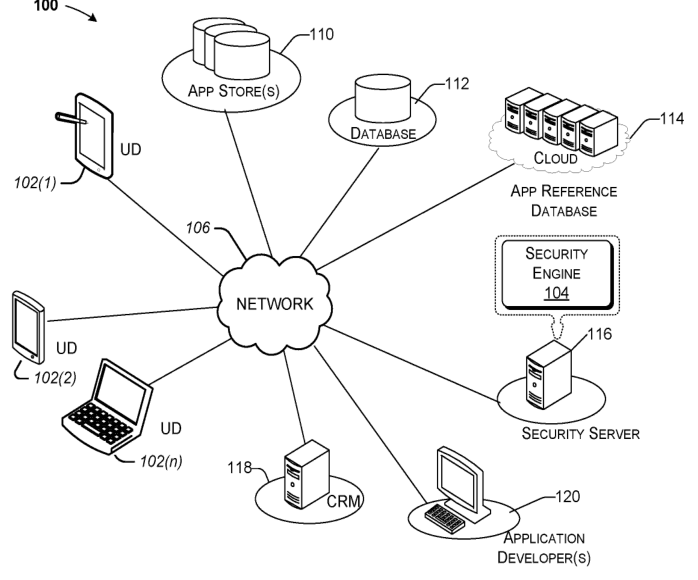
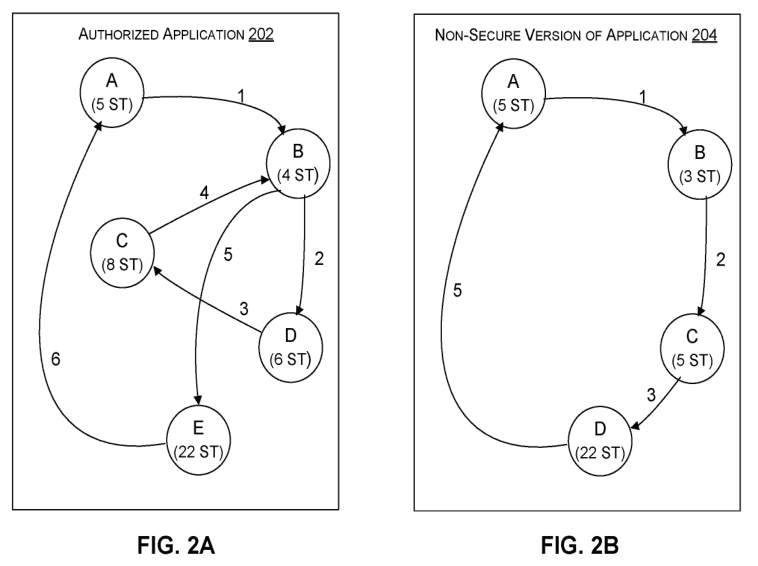
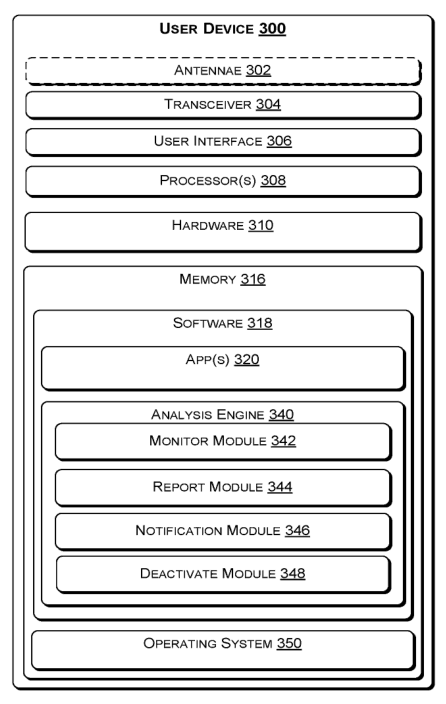
A method and system of determining a vulnerability of software are provided. In a setup phase, an authorized application is received from an authorized source. Static analysis is performed to identify a plurality of structural characteristics, which are stored. During an active phase, a call is received from a user device having a target application purporting to be a version of the authorized application, during a runtime of the target application. One or more structural characteristics are selected from the plurality of structural characteristics. The user device is requested to provide the selected one or more structural characteristics from the target application. Upon determining that the report does not provide a match between the selected one or more structural characteristic of the authorized application and the target application, the version of the target application is identified to be unsecure.
Full write-up available with Pro
Pro includes, for every patent on each weekly list: a written summary, the scope of the claims, materials and manufacturing route, a demand check with current listings and prices, and related-patent warnings.